
Spam protection
Every form falls victim to spambots at some point, and how you handle them can affect your customers.
Formspark offers the following solutions to prevent spam:
- Botpoison integration
- reCAPTCHA integration
- hCaptcha integration
- Turnstile integration
- Custom spam words
- Allowed domains
- Honeypot technique
On top of whichever of these you enable, every submission is screened by our automatic spam filtering, unless you switch it off for that form.
Formspark will not deliver a submission to your inbox, send notifications or decrement your submission counter if any of the following conditions are true:
- The submission is empty
- The challenge verification was unsuccessful
- The submission contains a honeypot
- The submission contains one of your custom spam words
- The submission was sent from a site that is not on your allowed domains
- The automatic filter flags the submission as spam
An empty submission is discarded. Every other rejected submission is kept for you to review. See rejected submissions.
Rejected submissions
A submission rejected as spam lands under Spam instead of Inbox. Open your form's Submissions and switch the view to Spam to see it. Hover its Spam tag to see what rejected it.
Rejected submissions stay there for up to 30 days. To recover one, use Mark as non-spam: it moves to your inbox and counts against your submission quota.
Your visitor sees an error for a rejected submission. A plain HTML form shows the error page, or your error redirect if you set one. An AJAX request answers 403 with Rejected by spam protection.
Which should I pick?
| Provider | Visitor experience | Pricing | Strength |
|---|---|---|---|
| Botpoison | Invisible | Free / paid | Strong |
| Turnstile | Invisible | Free | Strong |
| hCaptcha | Checkbox | Free | Strong |
| reCAPTCHA | Checkbox | Free | Strong |
| Custom spam words | Invisible | Included | Low |
| Allowed domains | Invisible | Included | Low |
| Honeypot | Invisible | Included | Low |
If you're not sure, start with Botpoison or Turnstile: both are invisible to your visitors and require no interaction.
Botpoison
Formspark integrates with Botpoison, an invisible, user-friendly anti-spam solution.
Getting started
- Go to https://botpoison.com/start/.
- Create a new configuration.
- Integrate the
public keyon your website (instructions). - Copy the
secret key. - Open Formspark.
- In your form's settings, under
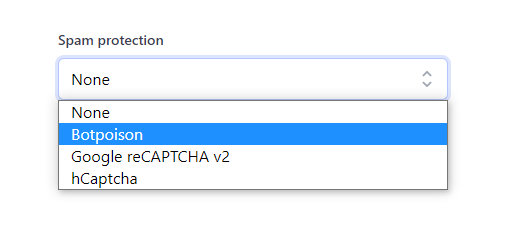
Spam protection, openChallengeand selectBotpoisonas theProvider. - Paste the
secret keyinto theBotpoison secret keyfield.
Your form is now protected by Botpoison ✔.
To stop using Botpoison, set the Provider under Challenge back to None.
Example
<!DOCTYPE html>
<html lang="en">
  <head>
    <script src="https://unpkg.com/@botpoison/browser" async></script>
  </head>
  <body>
    <form
      method="POST"
      action="https://submit-form.com/your-form-id"
      data-botpoison-public-key="your-botpoison-public-key"
      target="_blank"
    >
      <textarea name="message" placeholder="Message"></textarea>
      <button type="submit">Send</button>
    </form>
  </body>
</html>
AJAX
If you're using AJAX, add the Botpoison response to your submission body via the _botpoison property.
const body = {
  email: "john.doe@example.com",
  message: "Hello, World!",
  _botpoison: "...",
};
Recommended libraries
- JavaScript: @botpoison/browser
reCAPTCHA
Formspark integrates with Google's reCAPTCHA v2 "I'm not a robot" checkbox.
Getting started
- Go to https://www.google.com/recaptcha/.
- Navigate to the admin console.
- Create a new site.
- Make sure you select
reCAPTCHA v2. - Make sure you whitelist your website's domain.
- Integrate the
site keyon your website (instructions). - Copy the
secretkey. - Open Formspark.
- In your form's settings, under
Spam protection, openChallengeand selectreCAPTCHA v2as theProvider. - Paste the
secret keyinto thereCAPTCHA v2 secret keyfield.
Your form is now protected by reCAPTCHA ✔.
To stop using reCAPTCHA, set the Provider under Challenge back to None.
HTML
Make sure your form's method attribute is explicitly set to POST.
<form method="POST">...</form>AJAX
If you're using AJAX, add the reCAPTCHA response to your submission body via the g-recaptcha-response property.
const body = {
  email: "john.doe@example.com",
  message: "Hello, World!",
  "g-recaptcha-response": "...",
};
Recommended libraries
- React: react-google-recaptcha
Articles
hCaptcha
Formspark integrates with hCaptcha, an independent alternative to Google's reCAPTCHA.
Getting started
- Go to https://www.hcaptcha.com/.
- Create a new site.
- Integrate the
site keyon your website (instructions). You can find your site key here. - Copy the
secret key. You can find your secret key here. - In your form's settings, under
Spam protection, openChallengeand selecthCaptchaas theProvider. - Paste the
secret keyinto thehCaptcha secret keyfield.
Your form is now protected by hCaptcha ✔.
To stop using hCaptcha, set the Provider under Challenge back to None.
HTML
Make sure your form's method attribute is explicitly set to POST.
<form method="POST">...</form>AJAX
If you're using AJAX, add the hCaptcha response to your submission body via the h-captcha-response property.
const body = {
  email: "john.doe@example.com",
  message: "Hello, World!",
  "h-captcha-response": "...",
};
Recommended libraries
- React: react-hcaptcha
Turnstile
Formspark integrates with Turnstile, Cloudflare's smart CAPTCHA alternative.
Getting started
- Go to https://www.cloudflare.com/products/turnstile.
- Create a new site.
- Integrate the
site keyon your website (instructions). - Copy the
secret key. - In your form's settings, under
Spam protection, openChallengeand selectTurnstileas theProvider. - Paste the
secret keyinto theTurnstile secret keyfield.
Your form is now protected by Turnstile ✔.
To stop using Turnstile, set the Provider under Challenge back to None.
AJAX
If you're using AJAX, add the Turnstile response to your submission body via the cf-turnstile-response property.
const body = {
  email: "john.doe@example.com",
  message: "Hello, World!",
  "cf-turnstile-response": "...",
};
Recommended libraries
- React: react-turnstile
Automatic spam filtering
On top of any provider you choose, Formspark screens every submission for spam. It is on for every new form, requires no setup, and is invisible to your visitors.
The filtering is powered by Botpoison Classify, and you do not need a Botpoison account for it. It complements the challenge you select above rather than replacing it.
Switching it off
Under Spam protection in your form's settings, open Automatic filter and turn off Screen submissions for spam.
Two things change for that form when you do:
- Every submission is delivered, including the ones the filter would have held back. Each of those counts against your submission quota, where a filtered submission costs you nothing.
- Filtered submissions no longer appear under
Spam, which is where you would otherwise recover one the filter judged wrongly.
Your honeypot, custom spam words and chosen provider are unaffected and keep running.
Custom spam words
Custom spam words let you block submissions that contain specific words.
We scan the fields your visitor filled in for the words you specify. Matching ignores case and also finds a word inside a longer one. If a word is found, the submission is rejected as spam.
Fields your visitor did not write are skipped: control fields such as _redirect, challenge responses such as g-recaptcha-response, and tracking fields such as UTM tags (utm_source) and ad click ids (gclid, fbclid).
You specify the comma-separated list of words in your form's settings, under Spam protection in Spam words.
The total length of the list must not exceed 2,560 characters.
Allowed domains
List the sites your form lives on, and submissions sent from anywhere else are rejected as spam. Set it in your form's settings, under Spam protection in Allowed domains. It is off until you add a domain.
- Each domain also covers its subdomains:
example.comallowswww.example.comandshop.example.com. - You can paste a full address.
https://www.example.com/contactis saved asexample.com. - Submissions sent from a server, or by a tool such as
curl, are rejected, because they do not say which site they come from. - To test on your own machine, add
localhostto the list.
Honeypot
WARNING
While simple to implement, this technique is not the most effective. Modern spam bots that execute JavaScript can detect hidden fields and skip them, bypassing the honeypot entirely. Pair it with another provider above for serious protection.
The honeypot technique is a simple-to-implement spam prevention solution.
To enable this feature, add a field with the name _honeypot or _gotcha to your form and hide it with CSS (see example below). When a spam bot enters a value, the submission is rejected as spam.
<form action="https://submit-form.com/your-form-id" method="POST">
  <input
    type="checkbox"
    name="_honeypot"
    style="display:none"
    tabindex="-1"
    autocomplete="off"
  />
  <input type="email" name="email" />
  <button type="submit">Subscribe</button>
</form>
Custom honeypot
Besides _honeypot and _gotcha, you can specify your own honeypot name in your form's settings, under Spam protection in Honeypot. Enter it in the Custom field name field. The name must match your field's name exactly, including case.
<form action="https://submit-form.com/your-form-id" method="POST">
  <input
    type="checkbox"
    name="Paste your custom honeypot here"
    style="display:none"
    tabindex="-1"
    autocomplete="off"
  />
  <input type="email" name="email" />
  <button type="submit">Subscribe</button>
</form>